read receipts
Why Scammers Started Mailing You Pictures of Links
A QR code in an email isn't there to save you a step. It's there to hide the destination from you — and, in some products, from the scanner too.
A link scanner is a simple, relentless thing. It reads the text URLs in an email, checks them against lists of known-bad domains, follows redirects and flags the ones that lead somewhere nasty. It is good at its job. So scammers did the obvious thing: they stopped sending links.
They started sending pictures of links.
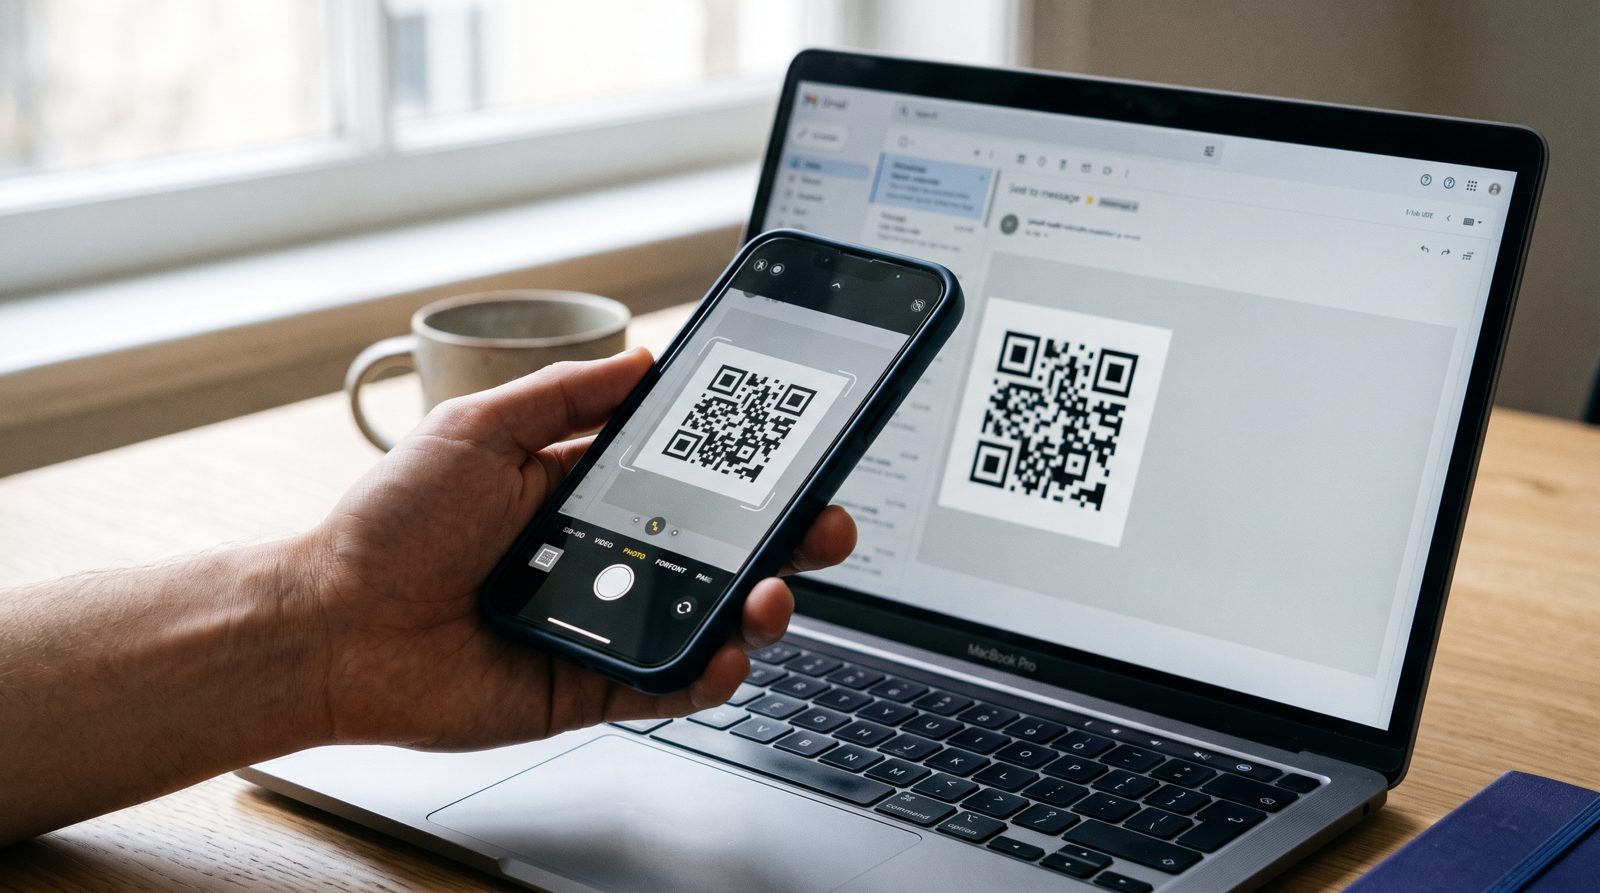
That is the trick behind "quishing" — QR-code phishing. A QR code is a URL encoded as a black-and-white image, so a destination like login-verify.example stops being text in the message body and becomes pixels. The point is not that the address is encrypted; anyone's camera decodes it instantly. The point is that it is no longer written anywhere you, or a text parser, can read before you commit.
Whether a filter can still read it depends entirely on the product. The UK's National Cyber Security Centre puts the limit in careful words in its February 2024 note on QR codes: "Not all security tools designed to detect phishing emails will scan images." Note what that does not say. It does not say none of them do. Microsoft published the other side of it in November 2024: Defender for Office 365, it wrote, "has improved its capabilities to extract URLs from QR codes," using image processing early in mail flow to "extract and log URLs hidden within QR codes," and it now also extracts QR metadata and looks for the surrounding pattern — minimal body text, a brand lure, a redirect chain. So "the filter can't read it" was true of many products for a while, is still true of some, and is not a law of nature. If you want to know whether it is true of your own mail, that is a question about your provider's product and configuration, not about QR codes.
The numbers that are checkable come from the same vendor, and they are worth reading with the scope attached. Microsoft's November 2024 post describes a surge with "some attacks increasing at a growth rate of 270% per month," says that "at the height, Defender for Office 365 was blocking 3 million attempts daily," and that after the detection work shipped "we have seen this number shrink to 200,000 QR code phishing attempts every day." Microsoft's Digital Defense Report 2026 puts a total on the current scale: 145+ million QR-code phishing attacks detected between July 2025 and June 2026 by Defender for Office 365. All of those figures are one vendor's telemetry for its own product, self-reported. They are not a share of all phishing, and they are not an industry total — an earlier version of this article cited a 25% share that no Microsoft publication appears to support, and that figure has been removed rather than replaced.
What makes the technique durable is the handoff, not the encoding. The email lands on a laptop, where the corporate filter, the managed browser and the password manager live. The code gets scanned on a phone, which is usually a personal device. The NCSC lists this among the reasons criminals favour the method: "Personal devices may not have the same security protections as a computer that's provided by your employer." On a phone the address bar truncates, the full URL is hard to inspect, and a password manager that would have refused to autofill on the wrong domain is not involved at all.
The themes are boringly predictable, which is a tell in itself, and they show up in the consumer warnings almost word for word. The FTC's December 2023 alert describes scammers covering the real QR code on a parking meter with their own sticker, and warns plainly: "Don't scan a QR code in an email or text message you weren't expecting," especially one that pushes you to act immediately. The FBI's IC3 public service announcement from January 2022 says the same about tampering — "Cybercriminals tamper with both digital and physical QR codes to replace legitimate codes with malicious codes" — and tells people to check physical codes for "a sticker placed on top of the original code." A code to re-enable expiring multi-factor authentication, a signature request you were not expecting, a shipping notice asking you to confirm delivery: the design goal is always a small, plausible reason to lift the phone before anything is checked.
So the defensive moves are the dull ones, and they are the ones the agencies actually publish. IC3's advice, for a message that wants a payment or a login after a scan: "call the company to verify," using "the company's phone number through a trusted site rather than a number provided in the email," and "avoid making payments through a site navigated to from a QR code. Instead, manually enter a known and trusted URL." Nothing about that requires you to judge whether a particular square is malicious — which is the part no human is good at.
One thing a QR code in an email never tells you is whether the message was forged. Domain authentication answers a different question entirely, and the current DMARC specification explicitly puts "content analysis" outside its scope — which is why a fully authenticated message can carry a malicious image. That mechanism is worth its own read, and it is the subject of a companion article in this series.
Correction, 20 October 2026. An earlier version of this article said that a spam filter cannot read a QR code and that scanners are blind to the encoded address. That is true of some email security products and not of others: Microsoft documented URL extraction from QR codes in Defender for Office 365 in November 2024, and the NCSC's wording is that not all tools scan images. The article also cited a figure of roughly 25% of email phishing using QR codes, attributed to Microsoft; no Microsoft publication supporting that share could be found, so the figure has been removed and replaced with figures Microsoft publishes directly, with their product and period stated. A demonstration phishing domain that had been rendered as a live link has been replaced with a non-clickable example on the reserved .example namespace, and a citation to the CISA home page has been replaced with the specific FBI IC3 and FTC advisories.
Sources
- Microsoft Security Blog — How Microsoft Defender for Office 365 innovated to address QR code phishing attacks — 4 November 2024. URL extraction from QR images; 270% monthly growth, 3 million daily attempts at peak, 200,000 daily after rollout
- Microsoft Digital Defense Report 2026 — 145+ million QR-code phishing attacks detected by Defender for Office 365, July 2025 – June 2026
- UK NCSC — QR Codes: what's the real risk? — Dave Chismon, 8 February 2024. "Not all security tools designed to detect phishing emails will scan images"; personal devices lack employer protections
- FTC — Scammers hide harmful links in QR codes to steal your information — Consumer alert, 6 December 2023, by Alvaro Puig. "Don't scan a QR code in an email or text message you weren't expecting"
- FBI IC3 — Cybercriminals Tampering with QR Codes to Steal Victim Funds — Public service announcement I-011822-PSA, 18 January 2022. Verification steps and the advice to enter a trusted URL manually